How AI coding tools could amplify software supplychain attacks
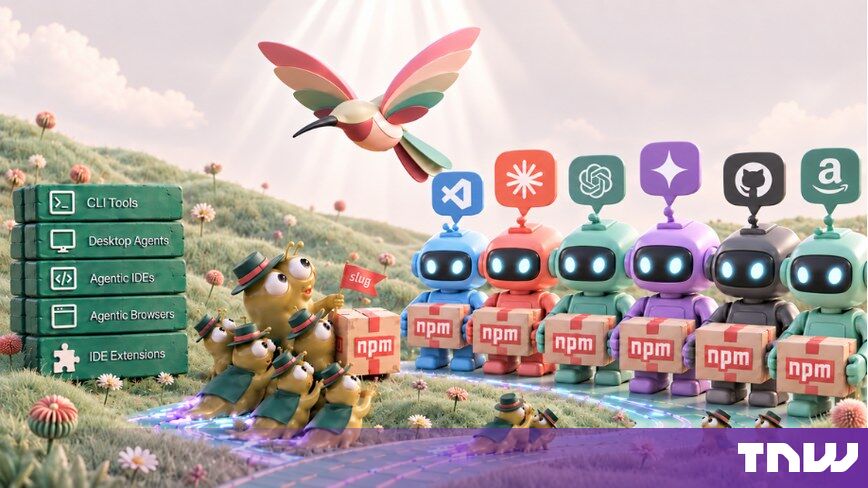
News Source : The Next Web
News Summary
- AI agents increasingly select, install, and execute code on their behalf.
- This activity creates more opportunities for untrusted code to enter an environment.
- A vulnerability in software publishing infrastructure can intersect with these automated workflows.
- Bloom Security identified more than 1,500 packages vulnerable to a publishing attack involving GitHub repository addresses.
- They had over 10 million combined downloads and more than one million downloads per month.
- It does not depend on stealing the legitimate maintainer’s credentials or compromising their GitHub account.
AI coding tools are changing how developers obtain and use software. But the growing volume of automated package installations is creating new challenges for enterprise security teams.









 Never miss a story from us, subscribe to our newsletter